
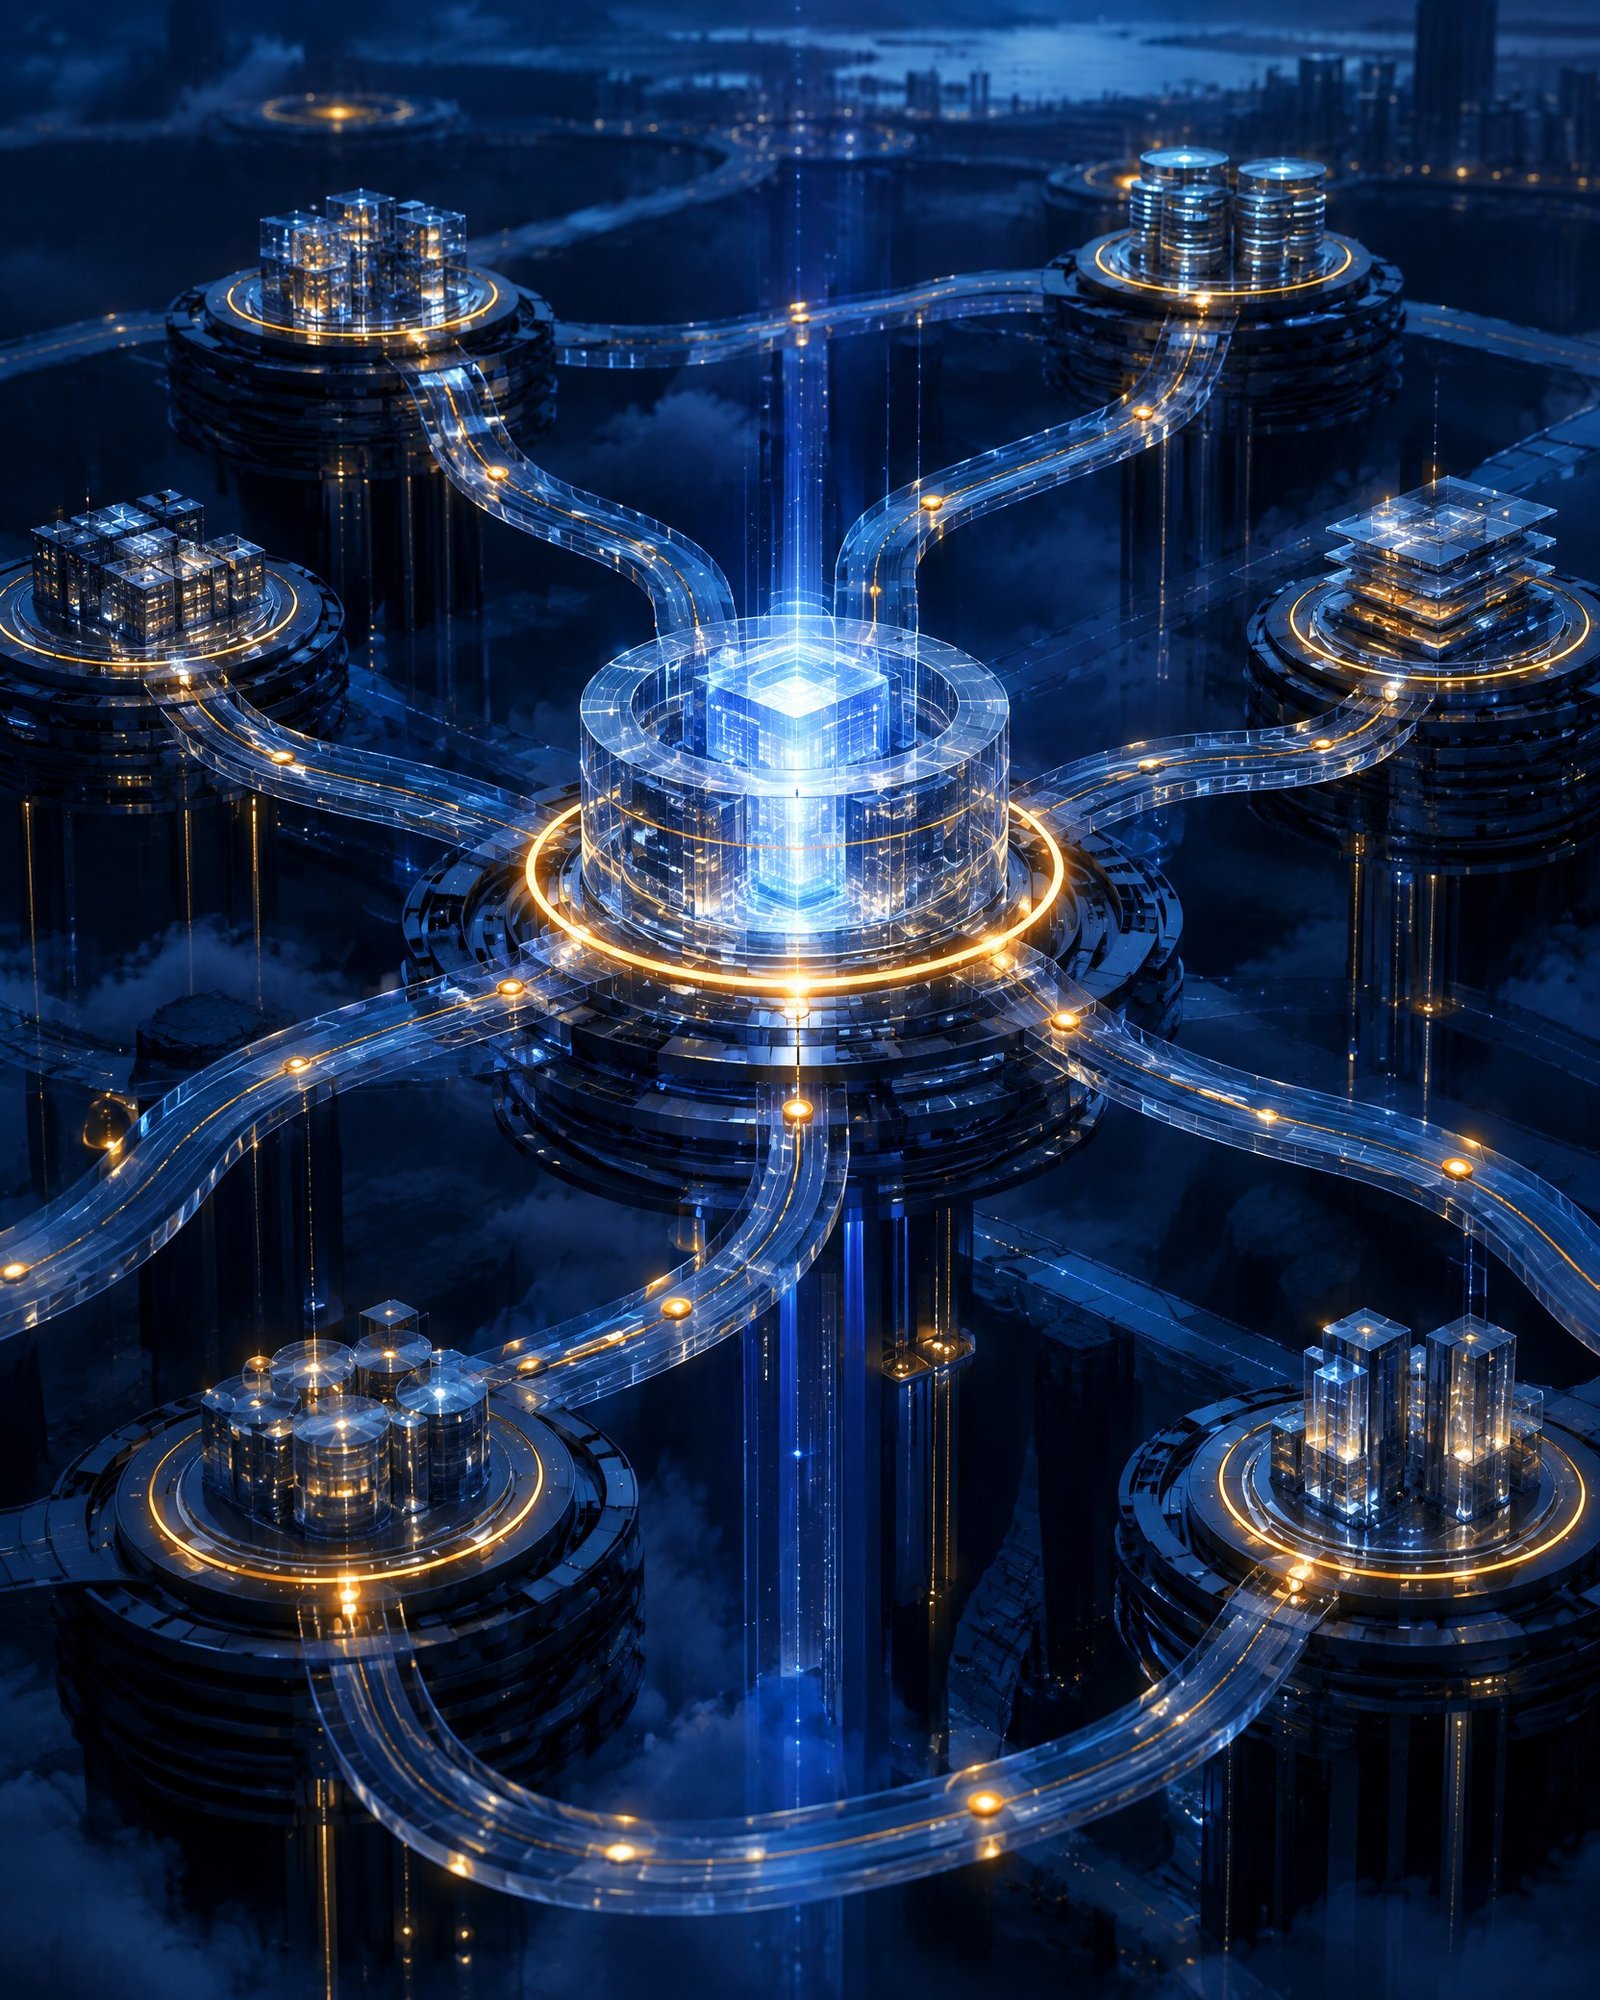
Digital Operational Resilience & ICT Third-Party Risk Governance in Bangladesh
We advise banks, financial institutions, payment providers, insurers, telecom operators, listed companies and technology exporters on digital operational resilience in Bangladesh: ICT governance, cloud and outsourcing contracts, regulator expectations, incident response, testing, exit planning and the contractual flow-down of overseas resilience rules.

- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Digital operational resilience for Bangladesh businesses
Digital operational resilience is the ability of an organisation to keep critical services running, or restore them quickly, when technology fails, a supplier collapses or an attacker gets in. For Bangladeshi banks, payment providers, insurers, telecom operators and large corporates, that ability now depends heavily on third parties: cloud platforms, core banking vendors, card processors, data centres and managed service providers. Our technology, IP and data team helps boards and management turn regulatory expectations and commercial risk into clear governance, workable contracts and incident plans that hold up when tested in practice.
Bangladesh does not have a single statute equivalent to the European Union's Digital Operational Resilience Act. Instead, obligations come from several directions. Bangladesh Bank issues ICT security guidelines and circulars for banks and financial institutions covering governance, risk management, outsourcing, cloud, business continuity and incident reporting. Payment system operators and providers face licence conditions of their own. Cyber security legislation, the Personal Data Protection Act 2026 and sector rules from the securities, insurance and telecommunications regulators add further layers. Digital operational resilience in Bangladesh therefore means mapping these sources together rather than reading any one in isolation.
Third-party risk is where most resilience programmes succeed or fail. A regulated entity remains responsible for a service even when a vendor performs it, so contracts must give the entity the information, access, audit rights, security standards, incident notification, subcontracting controls and exit support that regulators expect. Many standard vendor terms do not provide these. We review and negotiate ICT and cloud agreements against the applicable guidelines, identify where a vendor will not move, and help clients document compensating controls and risk acceptance so that the board's decision is recorded and defensible if questioned later by an inspector.
Overseas rules also reach Bangladesh. Technology, software and business process outsourcing companies serving European banks and insurers now receive contract terms reflecting EU digital operational resilience requirements, including audit rights, incident cooperation, testing participation, data location and termination assistance. Similar expectations arrive from UK, Singapore and Gulf financial regulators. We help Bangladeshi providers understand what those clauses demand, price the obligations realistically, and push back where a customer asks for more than the regulation requires. Getting this right protects margins and reduces the risk of disputes with important foreign clients. Digital operational resilience clauses deserve that care.
When something does go wrong, the legal response must move as fast as the technical one. Outages, ransomware, data breaches and vendor insolvency raise questions of regulator notification, customer communication, evidence preservation, insurance, contractual claims and sometimes criminal complaints. We support clients through those events and the reviews that follow, working with forensic and technical advisers and, where claims arise, with our dispute resolution practice. Strong digital operational resilience is ultimately a matter of preparation, so we also help clients rehearse incidents, refresh playbooks and test whether their contracts and escalation routes work under realistic pressure.
Core workstreams
Four clear stages
- 01Map services and rules
- 02Prioritise and remediate
- 03Prepare and test
- 04Respond and review
Talk to a partner
Consultations in Dhaka or by video. Scope, team and fees are agreed in writing first.
Book →Our resilience and third-party risk work

Governance and board oversight
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Third-party and cloud contracts
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Register of critical dependencies
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Incident readiness and response
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Testing, audit and assurance
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Overseas resilience flow-downs
- Map services and rules
- Prioritise and remediate
- Prepare and test
- Respond and review
Governance and board oversight
We help boards and senior management define responsibility for ICT risk, set risk appetite for critical services and technology dependencies, and establish reporting lines that meet Bangladesh Bank and other regulator expectations. We draft or review ICT governance policies, committee terms of reference and reporting templates, so that directors can later show they understood material dependencies and approved the key risk decisions on an informed basis.
Third-party and cloud contracts
We negotiate core banking, card processing, cloud, data centre, managed security and software agreements with a focus on service levels, security obligations, audit and access rights, regulator access, data location, subcontracting, incident notification, business continuity commitments and exit assistance. Where a large vendor offers only standard terms, we identify the gaps, propose addenda and help the client document any residual risk it decides to accept and why.
Register of critical dependencies
We help organisations build and maintain a register of ICT third-party arrangements that identifies critical and important functions, concentration risk, fourth-party dependencies and contract status. The register supports regulatory reporting, board oversight and procurement decisions, and shows quickly which contracts need renegotiation when guidelines or vendors change. We align legal fields in the register with what regulators and auditors typically ask to see during inspection.
Incident readiness and response
We prepare incident response playbooks covering regulator notification, customer and media communication, law enforcement contact, evidence preservation, insurer notice and contractual claims against vendors. During a live incident we provide legal coordination alongside technical responders, help manage privilege, and advise on obligations under cyber security law and the Personal Data Protection Act 2026, keeping decisions documented for later review. Good digital operational resilience depends on this preparation.
Testing, audit and assurance
We advise on the legal side of resilience testing, including scenario exercises, penetration testing engagements, red-team authorisations and audit of vendors. That includes scoping letters, confidentiality, liability for testing-related disruption and handling of findings. We also help clients respond to regulator inspection observations and internal audit reports, agree remediation plans, and track commitments so that issues are closed properly rather than repeated.
Overseas resilience flow-downs
For Bangladeshi technology and outsourcing companies, we review customer contracts reflecting EU, UK, Singapore or Gulf resilience rules, explain what each obligation requires in practice, and negotiate proportionate positions on audit, testing, subcontracting, incident reporting and termination. We help providers build reusable contract positions and internal procedures so they can respond quickly to future requests from regulated customers abroad. This makes digital operational resilience a selling point.
Partner-led, on every matter.
Technology, IP & Data matters at TRW are led by partners, supported by associates, with one responsible lawyer from first advice to final outcome.
Meet the firm →

01Is there a Bangladesh law on digital operational resilience like the EU's DORA?
Not as a single statute. For banks and financial institutions, the main source is Bangladesh Bank's ICT security guidelines and related circulars, which address governance, risk management, outsourcing, cloud, business continuity and incident reporting. Payment providers have licence-based requirements, and the securities, insurance and telecommunications regulators issue their own rules. Cyber security legislation and the Personal Data Protection Act 2026 apply more widely. In practice, digital operational resilience in Bangladesh is assembled from these sources, which is why a clear map of which rules apply to which service is the essential first step for any compliance programme.
02We are a Bangladeshi bank using a foreign cloud provider. What should the contract contain?
At a minimum, the contract should give the bank clear service levels, defined security standards, the right to audit or rely on independent assurance reports, access for Bangladesh Bank, prompt incident notification, controls on subcontracting, data location and segregation commitments, business continuity and disaster recovery obligations, and meaningful exit assistance with data return. Bangladesh Bank approval or notification may also be needed for certain cloud and outsourcing arrangements. We compare the provider's terms with these requirements, negotiate what can be negotiated and help the bank document compensating controls for what cannot be changed. That supports digital operational resilience.
03How does EU digital operational resilience regulation affect Bangladeshi IT companies?
The EU regime applies directly to European financial entities, not to Bangladeshi providers. However, those entities must include specific terms in contracts with ICT service providers, so Bangladeshi software, BPO and managed service companies serving them receive detailed clauses on security, audit, incident cooperation, testing, subcontracting, data location and exit. Accepting these terms without review can expose a provider to uncapped liability and heavy audit costs. We explain which requests are genuinely required, which go further than needed, and how to price, cap and limit the obligations so the relationship remains commercially sustainable for both sides.
04What should we do in the first hours of a serious ICT incident?
Contain the incident, preserve evidence and convene the response team, including legal. Early legal tasks include assessing whether regulators, customers or data subjects must be notified and when, notifying insurers, preserving logs and communications, controlling external statements, and checking vendor contracts for notification and cooperation duties. Privilege should be considered when forensic experts are engaged. Decisions should be recorded with reasons, because regulators and courts will later examine what management knew and when. A prepared playbook makes these first hours far more manageable and reduces the risk of inconsistent statements. Digital operational resilience depends on rehearsal.
05Can we rely on a vendor's standard terms for critical services?
Sometimes, but only after checking them against the regulatory expectations that apply to the service. Large global vendors often refuse bespoke drafting, yet many offer financial services addenda that cover audit, regulator access and exit. Where gaps remain, the board or a delegated committee should decide whether to accept the risk, seek an alternative provider or add compensating controls such as stronger monitoring, additional backup or a secondary provider. Regulators generally expect that decision to be informed and documented. Digital operational resilience is weakened most when critical contracts are signed without anyone recording what was missing.
06What is concentration risk, and why do regulators care about it?
Concentration risk arises when many critical services depend on a single provider, data centre, network or platform, or when much of a sector relies on the same few vendors. A failure at that point can disrupt many functions at once. Regulators increasingly ask firms to identify and manage these dependencies, including fourth parties behind their direct vendors. For digital operational resilience planning, this means understanding where alternatives exist, how quickly services could move, and whether contracts support a realistic exit. We help clients map concentration risk and reflect it in procurement decisions and board reporting.
07How should exit and termination be handled in ICT outsourcing contracts?
Exit planning should start before signing. The contract should require the vendor to provide transition assistance, return data in usable formats, continue service for an adequate period after termination, and cooperate with a successor provider. Escrow of source code may be relevant for critical software. Termination rights should cover regulatory direction, serious security failures and change of control. Without these protections, an organisation can be locked in to a failing provider. We draft exit provisions, including data return formats, and help clients prepare practical exit plans that regulators can review and that operational teams can actually follow.
08Do digital operational resilience obligations apply to non-financial companies?
Formal regulatory obligations are heaviest in banking, payments, capital markets, insurance and telecommunications. Other businesses face resilience duties through cyber security legislation, particularly where systems are designated as critical information infrastructure, and through data protection law, customer contracts and directors' general duties of care. Exporters, manufacturers and hospital groups increasingly receive resilience requirements from overseas customers and insurers. For these organisations, the same disciplines of governance, contract control, incident readiness and exit planning reduce disruption and the legal exposure that follows a serious outage. Digital operational resilience is a shared discipline across all sectors.
From first call to resolution.
- 01
Map services and rules
We identify critical services, the technology and third parties behind them, and the Bangladesh and overseas rules that apply, producing a clear picture of where digital operational resilience obligations and gaps sit. The map becomes the baseline for later work.
- 02
Prioritise and remediate
We rank gaps by regulatory and operational risk, then renegotiate key contracts, update policies and governance documents, and agree a realistic remediation plan with management and the board. Owners and deadlines are assigned for each action. Progress against the plan is reported to the board at agreed intervals so that overdue items are visible.
- 03
Prepare and test
We build incident playbooks, support scenario exercises and testing engagements, and refine notification, communication and evidence procedures based on what each exercise reveals about readiness. Each test strengthens digital operational resilience and leaves a record.
- 04
Respond and review
When incidents or inspections occur, we advise in real time, manage regulator and counterparty communications, pursue or defend claims, and feed lessons back into contracts and governance. Reviews keep digital operational resilience current as the business changes. We also brief the board.

“Demonstrates an extraordinary command over both domestic litigation and international arbitration.”
The Legal 500 Asia Pacific, Bangladesh: Dispute resolution, client feedback
Related reading.
Cyber Law Compliance in Bangladesh 2026: A Business Checklist under the Cyber Security Act
Bangladesh Data Protection Law: 2026 Guide
Bangladesh Banking Regulations: A Practical 2026 Guide
PSO and PSP Licence in Bangladesh 2026: Payment Licensing, E-Money, Digital Banks and the Financial Regulators
All insights →
Who in an organisation is responsible for digital operational resilience?
Does Bangladesh Bank need to approve cloud outsourcing?
How often should our incident response plans be tested, and by whom?
Can we recover our losses from a technology vendor after a serious outage?
What is fourth-party risk, and how can contracts control it?
Are personal data breaches treated differently from system outages under Bangladesh law?
Can TRW help a Bangladeshi IT exporter with digital operational resilience clauses?
How do we start a digital operational resilience review with TRW?
Strengthen your resilience before the next incident
Speak with the partners about digital operational resilience in Bangladesh or across borders.
Book a consultation →